
In an era where digital security is paramount, 101domain is proud to announce a significant milestone in our commitment to safeguarding client data and services: the successful completion of our independent System and Organization Controls (SOC 2® Type I) audit. This achievement underscores our dedication to maintaining the highest industry standards for security and operational integrity, providing an essential layer of trust and assurance for our valued clients. As a leading domain registrar, protecting your critical online assets – your domain names – from malicious activities like hijacking and unauthorized access is at the core of our mission. This SOC 2® certification is not just a badge; it’s a testament to the robust controls and comprehensive safeguards we have meticulously implemented to protect your digital presence.
The successful completion of this rigorous audit signifies that 101domain’s systems and processes meet the stringent requirements set forth by the American Institute of Certified Public Accountants (AICPA). It provides an objective, third-party validation that our internal controls align with industry best practices, ensuring the security, availability, processing integrity, confidentiality, and privacy of the data we handle on your behalf. For businesses operating in today’s complex digital landscape, partnering with a SOC 2® compliant registrar offers peace of mind, knowing that your domain portfolio is managed with an unwavering commitment to security excellence.
Understanding SOC 2 Certification and Its Impact on 101domain
Achieving SOC 2® Type I certification means that 101domain has undergone and passed an intensive, independent audit conducted by a Certified Public Accounting (CPA) firm. This audit meticulously examined the design and implementation of our internal controls related to how we manage and protect client data and services. It’s a thorough evaluation, not merely a self-assessment, which provides an unbiased report on our security posture. For our clients, this translates into tangible benefits, offering robust assurance that their invaluable domain names and associated data are in secure hands.
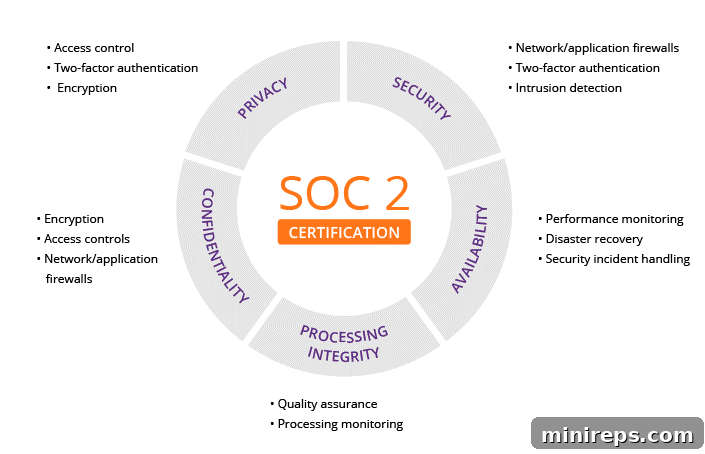
The SOC 2® framework is specifically designed for service organizations that store customer data in the cloud, making it particularly relevant for a domain registrar like 101domain. Service providers who successfully complete a SOC 2® audit demonstrably commit to, and execute on, a high level of technological and operational standards concerning five critical “Trust Service Principles.” These principles form the bedrock of data security and operational reliability in the digital age:
- Security: The protection of information and systems against unauthorized access, use, disclosure, modification, or destruction. For 101domain, this means safeguarding your domain management accounts and preventing unauthorized transfers or changes.
- Availability: The assurance that systems and information are available for operation and use as committed or agreed. Our commitment ensures that you can always access and manage your domains, and that our services are consistently online and responsive.
- Processing Integrity: Ensuring that system processing is complete, valid, accurate, timely, and authorized. This is crucial for critical domain operations such as registrations, renewals, DNS updates, and transfers, guaranteeing that your instructions are executed correctly.
- Confidentiality: The protection of information designated as confidential from unauthorized access or disclosure. This applies to sensitive client data and business information shared with us, ensuring it remains private and secure.
- Privacy: The collection, use, retention, disclosure, and disposal of personal information in conformity with the commitments in the entity’s privacy notice and with criteria set forth by relevant regulations (e.g., GDPR, CCPA). We adhere to strict privacy policies to protect your personal data.
Securing Your Business in the Digital Age with SOC 2 Audit
In today’s interconnected digital landscape, businesses increasingly rely on third-party service providers for critical operations. This reliance, while beneficial, introduces inherent risks if those partners do not uphold stringent security standards. Therefore, an SOC 2® audit has become more than just a recommendation; it is an essential requirement for robust corporate governance and effective vendor risk management. If your organization is not already evaluating key SaaS and technology vendors for SOC 2® compliance, we strongly encourage you to integrate this into your due diligence process.
For security-conscious businesses, particularly those operating in highly regulated industries such as finance (banks, credit unions), healthcare (medical service providers), or any sector handling sensitive customer data, evaluating technology partners for potential cybersecurity risks is paramount. A SOC 2® report provides an in-depth understanding of a service organization’s security controls, helping you make informed decisions and ensuring that your chosen partners meet your stringent compliance and security requirements. By choosing a SOC 2® compliant registrar like 101domain, you are actively mitigating risks associated with data breaches, service disruptions, and unauthorized access to your most valuable digital assets.
Why Choosing a SOC 2 Compliant Registrar Matters for Your Digital Trust
Your domain name is more than just an address; it’s your brand identity, your digital storefront, and often the first point of contact for your customers. Entrusting its management to a registrar requires absolute confidence in their security practices. The SOC 2 Type I certification is a clear signal that 101domain prioritizes this trust above all else. It assures you that:
- Your Data is Protected: Personal and business information you provide to us is handled under audited security controls, minimizing the risk of unauthorized access or exposure.
- Services are Reliable: Our systems are designed for high availability and processing integrity, meaning your domain services (registration, renewals, DNS management) will be consistently accessible and accurately executed.
- Risk is Mitigated: We proactively address cybersecurity threats, protecting your domains from common attacks such as hijacking, phishing, and malware propagation through compromised accounts.
- Compliance is Ensured: For businesses needing to comply with various regulatory frameworks (e.g., HIPAA, GDPR, PCI DSS), partnering with a SOC 2 compliant vendor simplifies your own compliance efforts.
- Transparency is Our Standard: The audit process itself emphasizes transparency, allowing us to openly share our security posture with you.
This commitment extends beyond initial certification. We are not resting on our laurels; our journey towards continuous security enhancement includes plans to pursue our SOC 2® Type II audit. While Type I provides a snapshot of our controls at a specific point in time, Type II evaluates the effectiveness of those controls over an extended period. This ongoing pursuit demonstrates our unwavering dedication to maintaining and improving our security framework, ensuring that 101domain remains a leader in secure domain management for years to come. We are committed to keeping you informed on our progress and thank you for your continued business and support as we grow and evolve together.
How Can You Review 101domain’s SOC 2 Report?
Transparency and trust are fundamental to our client relationships. We are pleased to provide copies of our comprehensive SOC 2® Type I report to existing clients, prospective clients, partners, and Registry suppliers upon request. This detailed security audit report offers an in-depth look at our control objectives and the specific processes we have implemented to meet the Trust Service Principles. To ensure the confidentiality of the sensitive information contained within the report, it is available after the execution of a Non-Disclosure Agreement (NDA). Please fill out the provided form on our dedicated page to formally request the report and gain further insight into 101domain’s robust security posture.