
Traditionally, June has been recognized as a relatively calm period for global news, including the fast-paced world of cybersecurity. However, recent events have decisively disrupted this trend. This past June witnessed an unprecedented surge in cybersecurity incidents, ranging from sophisticated data breaches and intricate hacking operations to large-scale Distributed Denial of Service (DDoS) attacks. These events collectively underscore a rapidly evolving digital threat landscape, demanding heightened vigilance and robust protective measures from individuals and organizations alike.
Unpacking the China DDoS Attack: Origins, Methods, and Impact on Global Cybersecurity
The cybersecurity community has been particularly focused on a series of high-profile incidents. The U.S. government recently confirmed a significant data breach involving a database of traveler photos, which had been compromised by hackers. Adding to these concerns, reports surfaced about another sophisticated hacker group actively probing the U.S. power grid for potential vulnerabilities. These incidents highlight the persistent and escalating threat of state-sponsored cyber espionage and infrastructure targeting.
Amidst these developments, arguably the most impactful cybersecurity story of the month was the large-scale DDoS attack specifically targeting Telegram Messenger. This attack, widely attributed to the Chinese government, saw the popular encrypted messaging service inundated with terabytes of malicious data over several consecutive days. The disruptive effects were profoundly felt by users across Hong Kong, mainland China, and even the United States, significantly hindering communication during a critical period.
While this was not the first time Telegram or similar platforms have faced such interference, this particular incident signaled a worrying escalation. It underscored China’s increasingly assertive posture in blocking and disrupting encrypted communication services, particularly those used by activists and protestors. Furthermore, it served as a stark demonstration of the immense power and sophisticated capabilities that China can leverage in orchestrating large-scale cyberattacks, raising significant concerns about digital sovereignty and freedom of expression online.
1. China’s Evolving Role in Global Cybersecurity and Internet Control
The targeted DDoS attack on Telegram illuminates a troubling trajectory in China’s approach to internet privacy and security. Hong Kong, traditionally operating under the “One Country, Two Systems” framework, has largely been exempt from the stringent internet censorship prevalent in mainland China. However, a growing number of activists and international observers have expressed profound concern regarding escalating pressure from Beijing aimed at curtailing the region’s digital freedoms and autonomy. This pressure directly correlates with efforts to control information flow, making encrypted platforms like Telegram a direct target.
Beyond Hong Kong, there are broader international anxieties regarding China’s pervasive influence over global IT infrastructure. The widely reported news of telecommunications giant Huawei being banned from Australia’s 5G network dominated headlines, reflecting concerns about potential backdoors and state-sponsored espionage in critical infrastructure. However, less prominent but equally alarming trends also contribute to this apprehension.
For instance, a comprehensive study examining the top 20 free VPN applications available on Google Play and the Apple App Store revealed that a significant majority are either registered as Chinese companies or were developed by Chinese entities. While the appeal of a cost-free VPN service is undeniable, cybersecurity experts frequently caution against their indiscriminate use. These free services often lack robust security protocols, may log user data, or even contain malware, effectively compromising the very privacy they promise to protect. Instead, professionals recommend consulting trusted third-party reviews of free VPNs that meticulously evaluate services beyond just Chinese-originated products, prioritizing user security and data integrity.
2. The Geopolitical Impetus Behind the China DDoS Attack on Telegram
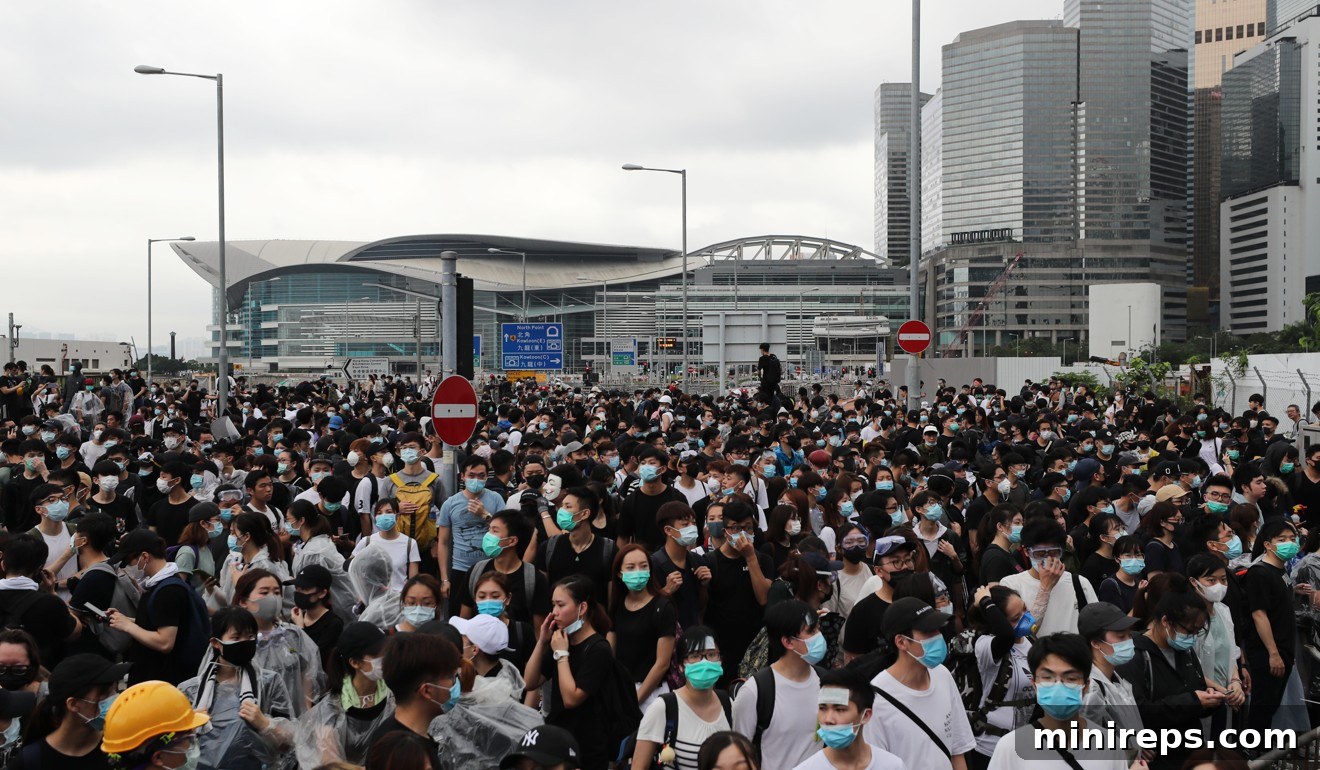
The motivation for the Telegram DDoS attack is clearly rooted in recent geopolitical developments. For several weeks leading up to the attack, Hong Kong had been gripped by a series of massive public protests. These demonstrations initially erupted in opposition to a highly controversial extradition bill, which, if passed, would have permitted the transfer of criminal suspects from Hong Kong to mainland China for trial. Critics argued this bill would severely undermine Hong Kong’s judicial independence and unique semi-autonomous status. What began as opposition to a specific piece of legislation quickly escalated into a much broader movement, encompassing demands for greater democracy, accountability for alleged police brutality, and a staunch defense of Hong Kong’s civil liberties against perceived encroachment from Beijing.
The intensity of these protests reached a crescendo when, last Wednesday, tens of thousands of demonstrators massed outside government headquarters, effectively paralyzing parts of the city. A crucial element enabling the organization and rapid coordination of these large-scale, often leaderless, protests was the widespread use of encrypted messaging services. Platforms such as WhatsApp, Signal, and particularly Telegram, became indispensable tools for activists to share information, organize rallies, disseminate updates, and mobilize participants while maintaining a degree of privacy and security.
Recognizing the pivotal role these secure communication channels played, the Chinese government, and its associated entities, took direct action to undermine their effectiveness and security. A notable incident, as reported by the South China Morning Post, involved the arrest of an administrator of a Telegram group. This individual was charged with ‘conspiracy to commit public nuisance,’ a move widely interpreted as a deliberate warning designed to intimidate and deter others from using the app for protest coordination. The DDoS attack on Telegram, therefore, was not merely an act of cyber vandalism but a strategic maneuver intended to suppress dissent and control information flow during a period of significant social unrest.
3. Detailing the Telegram DDoS Attack: Mechanics and Initial Response
The large-scale Distributed Denial of Service (DDoS) attack on Telegram was first publicly reported by Telegram itself on June 12th. While the company initially maintained a degree of reticence in officially identifying the source of the attack, it is highly probable that their internal security teams had indications pointing towards China from the earliest stages, given the geopolitical context and the nature of the traffic.
A DDoS attack is fundamentally designed to render an online service or website unavailable by overwhelming it with a flood of traffic from multiple compromised sources, often referred to as a botnet. This specific type of attack, known as a volumetric attack, typically involves sending millions upon millions of seemingly legitimate, but in fact, bogus service requests to a target server every second. The core objective is to saturate the server’s bandwidth and processing capabilities with so many illegitimate requests that it becomes utterly incapable of responding to genuine user requests, effectively locking out legitimate users and disrupting service.
Telegram, known for its direct and often humorous communication style, described the DDoS attack in a remarkably simplistic and relatable manner for its users. They posted a tweet inviting their community to:
“Imagine that an army of lemmings just jumped the queue at McDonald’s in front of you – and each is ordering a whopper. The server is busy telling the whopper lemmings they came to the wrong place – but there are so many of them that the server can’t even see you to try and take your order.”
This vivid analogy effectively communicated the overwhelming nature of the attack, and consequently, the incident quickly became widely known within the cybersecurity community and among users as the ‘whopper’ DDoS attack.
It was only after a few more days, as Telegram’s technical teams continued to analyze the overwhelming traffic patterns, that the company was prepared to explicitly identify the orchestrator. Telegram’s outspoken founder, Pavel Durov, took to Twitter to directly accuse the Chinese government of launching the massive cyber assault. His conclusion was founded on the sheer, unprecedented scale of the attack, which far exceeded typical criminal operations, coupled with the critical detail that the vast majority of the IP addresses originating the malicious traffic were traced back to mainland China. Durov was notably unequivocal in his statement, characterizing the event as a “state actor-sized DDoS,” and critically emphasizing that the timing of the attack directly coincided with the ongoing and intensifying protests in Hong Kong, thereby linking the cyberattack to clear geopolitical motivations.
4. Mitigating a State-Sponsored DDoS Attack: Telegram’s Resilience and User Implications
While the precise technical mechanisms employed to execute the state-sponsored DDoS attack on Telegram are unlikely to ever be fully disclosed, it is common knowledge that such large-scale disruptions are frequently associated with vast networks of compromised devices known as botnets. However, the immense resources and sophisticated capabilities at the disposal of a nation-state like the Chinese government mean that they are not necessarily restricted to relying solely on traditional botnets. They possess the capacity to leverage national internet infrastructure, specialized hardware, and potentially even direct control over large segments of internet traffic to launch attacks of unparalleled magnitude and complexity, making them incredibly difficult to defend against.
From a different vantage point, it’s crucial to examine Telegram’s response and what steps the service undertook to protect its users against such a formidable DDoS attack. In many respects, Telegram demonstrated remarkable resilience and technical prowess, performing admirably given the unprecedented scale and apparent state-level sponsorship of the assault. Their quick response and robust infrastructure were key to mitigating the long-term impact.
Telegram appeared to have stabilized after a few hours.
They assured users that their data is safe.
Ultimately, Telegram fulfilled its core promise as an encrypted messaging service. It allowed protestors and other users to exchange sensitive, encrypted information, even if this communication was temporarily disrupted for a few hours during the peak of the attack. This resilience, ensuring data integrity and eventual service restoration, was undoubtedly a source of profound frustration for the Chinese government, whose aim was to completely incapacitate the platform. It also explains why, as Bloomberg reported, encrypted messaging apps like Telegram experienced a significant surge in popularity and usage among Hong Kong residents during this tumultuous period.
From an individual user’s perspective, there is unfortunately very little one can do to directly protect themselves against a large-scale DDoS attack targeting the service provider itself, such as Telegram. The responsibility for defense lies primarily with the service provider’s infrastructure. However, for business owners, particularly those operating online, it is absolutely critical to take proactive measures to safeguard their digital assets. This includes implementing robust strategies to prevent DNS attacks, which are among the most common and damaging cyberattacks targeting small businesses. Investing in advanced DNS security, content delivery networks (CDNs), and cloud-based DDoS mitigation services can provide essential layers of protection, ensuring business continuity even when facing sophisticated threats.
The Bottom Line: Addressing the Implications of China’s DDoS Attack
For many years, the primary concern regarding Chinese cyber policy revolved around passive surveillance and espionage, where data collection and monitoring were the most worrying elements. However, the recent, audacious DDoS attack on Telegram Messenger signifies a dangerous and assertive shift in China’s approach to these issues. This incident demonstrates a move beyond mere surveillance; the government now appears confident enough to directly attack and disrupt the very services that facilitate independent communication and organization. This escalating aggression sets a troubling precedent for global internet freedom and underscores a new era of cyber warfare where communication platforms become battlegrounds.
In this heightened threat environment, it is no longer sufficient for online businesses and critical infrastructure providers to rely on basic cybersecurity measures. It has become absolutely essential to have comprehensive and advanced DNS and DDoS protection. Such protection involves multi-layered defenses, including real-time traffic analysis, anomaly detection, rate limiting, and scrubbing centers capable of filtering out malicious traffic before it reaches target servers. Proactive defense mechanisms are vital to ensure operational continuity, protect user data, and uphold digital rights in an increasingly complex and politically charged cyber landscape. The Telegram DDoS attack serves as a potent reminder that the digital realm is now a crucial arena for geopolitical maneuvering, where robust cybersecurity is not just a technical requirement, but a fundamental safeguard for freedom and stability.