
For e-commerce leaders and Chief Information Security Officers (CISOs), the login page has long been a point of tension. Digital commerce teams prioritize user experience (UX) and conversion rates, arguing that any friction drives customers away. Security teams face a steady stream of automated login attempts and demand stronger protections to safeguard accounts and corporate systems.
For years the industry relied on CAPTCHAs as a compromise: interactive puzzles intended to separate humans from bots. But by 2026 that compromise is failing. Advanced AI-driven bots can solve many traditional visual and textual CAPTCHAs quickly and accurately, while legitimate customers become frustrated and abandon carts or registrations.
To protect user identities and maintain trust, enterprises must shift from reactive, visible challenges to preventative measures that stop automated fraud before it reaches the authentication database—without imposing extra steps on real users.
The anatomy of modern credential stuffing
Credential stuffing is a form of account takeover fraud that exploits the widespread reuse of credentials. When a major service suffers a breach, large lists of leaked username and password pairs—so-called combo lists—circulate online.
Attackers use botnets to test those leaked credentials against login pages of high-value targets like e-commerce sites, loyalty programs, and corporate portals. Traditional defenses such as simple rate limits are less effective today because attackers use thousands of residential proxies to spread their requests. This “low-and-slow” approach makes malicious traffic look like many distinct, legitimate users.
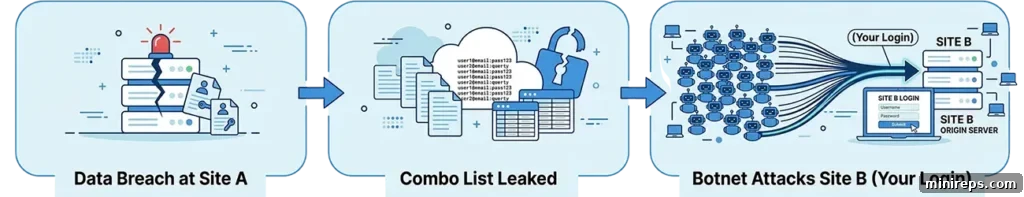
When an attacker finds valid credentials, the consequences can be severe: drained loyalty balances, stolen payment details, fraudulent purchases, or the resale of access to criminal groups. Stopping these attacks requires detecting compromised credentials and automated behavior before they reach account backends.
Inline intelligence: How Cloudflare Enterprise inspects credentials in-flight
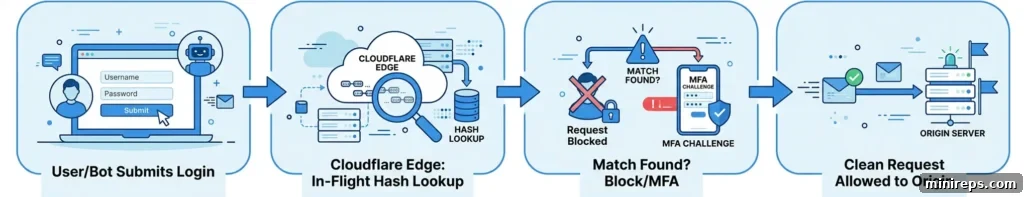
Rather than forcing users to solve puzzles or waiting for a bot to succeed, Cloudflare Enterprise inspects authentication attempts at the network edge using an Account Takeover Protection (ATO) ruleset.
This approach relies on a continuously updated global dataset of leaked credentials. When a login form is submitted, Cloudflare can evaluate the authentication payload at the nearest edge data center before the request ever reaches the origin application.
The CISO’s Question: What About Privacy?
Security teams commonly ask whether the provider sees users’ cleartext passwords. Cloudflare addresses privacy concerns with a blinded lookup process based on an Oblivious Pseudo-Random Function (OPRF). This preserves confidentiality while allowing a match against known leaked credentials.
- When a user submits credentials, the login page or the Cloudflare edge computes a one-way cryptographic hash of those credentials.
- Only a partial, privacy-preserving fragment of that hash is sent to query the leaked credentials dataset.
- The service returns a mathematical proof indicating whether that credential combination appears in the breach data, without exposing the password itself.
At no point are cleartext passwords stored or logged by the service, helping maintain compliance with privacy frameworks and industry standards.
Behavioral analysis over static challenges
Detecting compromised passwords is important, but it isn’t enough. To stop sophisticated, targeted attacks, Cloudflare Enterprise supplements credential checks with invisible behavioral analysis.
Instead of visible puzzles, the system evaluates hundreds of passive telemetry signals from the browser or application wrapper, including:
- Device fingerprinting: Comparing claimed device and browser signals to observed technical characteristics to detect headless scripts.
- Behavioral anomalies: Identifying form-fill speeds, mouse and touch patterns, and other interactions that are implausible for humans.
- Reputation scoring: Checking whether the browser identity or network ASN has recently been associated with credential stuffing attempts across the global network.
By combining credential matching with behavioral signals, each login attempt receives a real-time risk score that informs an appropriate automated response.
The business impact: Intelligent risk mitigation
When an attempt is flagged as high risk, the platform avoids blunt actions like immediately dropping traffic, which can tip off attackers. Instead, it enables configurable mitigation workflows that balance security and customer experience.
Typical actions include:
| Calculated Traffic Risk | Identity Status | Automated Action Taken at the Edge | Impact on Legitimate Customers |
|---|---|---|---|
| 🟢 Low Risk | Clean | Request passed immediately to origin database. | Zero Friction. Fast, seamless login. |
| 🟡 Medium Risk | Behavioral Anomaly | Trigger an invisible challenge to verify humanity without user interaction. | Zero Friction. Handled in the background in milliseconds. |
| 🟠 High Risk | Matched to Leaked Credentials | Inject a header to the origin to enforce Multi-Factor Authentication or a secure password reset flow. | High Security. Account is restricted until verified by the owner. |
| 🔴 Critical Risk | Confirmed Malicious Bot | Hard block or redirect to a honeypot to neutralize botnet activity. | Protected. Attacks are stopped before reaching infrastructure. |
This graduated, risk-based approach improves conversion on critical pages by minimizing friction for legitimate users while protecting authentication infrastructure from large volumes of malicious traffic. The result is better customer experience, lower server load, and reduced risk of financial or reputational damage from account takeovers.
Lock the front door with Cloudflare Enterprise
Security shouldn’t punish customers. Relying on legacy CAPTCHAs concedes that perimeter defenses can’t tell a genuine user from an automated attack. Moving authentication protections to the edge gives you global intelligence and the ability to stop automated fraud before it reaches your systems.
Cloudflare Enterprise edge controls let organizations apply real-time credential checks and behavioral analysis, preserving seamless logins for customers while neutralizing automated threats out on the network.