
The rules that underpin digital trust are changing again. For many years, the common maximum validity for a public SSL/TLS certificate was 398 days. As of March 15, 2026, that maximum has been reduced. The CA/Browser Forum, the industry body overseeing certificate policy, has mandated a new maximum validity of 200 days. This change begins a multi-year shift toward much shorter certificate lifespans, driven by major platform vendors such as Apple and Google to strengthen web security and encourage faster cryptographic updates.
This transition will affect organizations of all sizes. By shortening certificate lifespans, the industry reduces the window during which a compromised or misissued certificate can be abused. The plan is phased: after the 200-day cap, the maximum will drop to 100 days and eventually to 47 days by 2029 under current industry plans. These shorter cycles make manual certificate management increasingly impractical and increase the importance of automated discovery, monitoring, and renewal processes.
The roadmap to 47-day certificates
The shift to shorter certificate validity is being implemented in stages so organizations can adapt processes and tooling. The phased timeline gives teams time to build automation and revise operational procedures before each reduction in maximum validity.
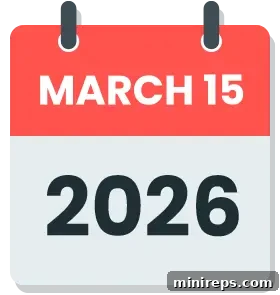
March 15, 2026 — the current 200-day limit becomes effective.
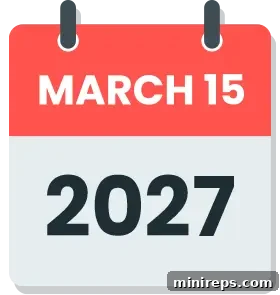
March 15, 2027 — the maximum validity will be reduced to a 100-day limit.
March 15, 2028 — the plan moves the internet toward 47-day certificate cycles as a long-term objective.
Although the formal cap is 200 days, many Certificate Authorities are issuing certificates with a 199-day validity. That single-day reduction provides a safety buffer to avoid accidental violations due to time zone differences or processing delays and ensures issued certificates comply with browser-enforced limits.
Why shorter certificate lifespans matter
Shorter certificate lifespans support two critical objectives: improved security and faster cryptographic agility. From a security standpoint, lowering the maximum validity reduces the exposure time for a compromised private key or a misissued certificate. Where certificates once could remain valid for more than a year, the new limits dramatically shrink the attack surface.
Cryptographic agility is the other major driver. As the industry moves toward new standards such as post-quantum algorithms, the ability to rotate certificates and adopt updated cryptography quickly becomes essential. Short validity periods mean servers and browsers worldwide can transition to new algorithms in months rather than years, enabling coordinated upgrades and reducing the lifespan of legacy, weaker cryptographic material.
The operational challenge of 200 days
At first glance, moving from yearly renewals to twice-yearly renewals may seem manageable. In practice, however, the margin for error narrows quickly. When the cap drops to 100 days and ultimately to 47 days, the frequency of renewal events increases substantially. Organizations that manage hundreds or thousands of certificates across business units will find manual tracking in spreadsheets unreliable and risky.
A single missed renewal can cause website outages, API failures, or browser trust warnings. The resulting downtime and reputational damage can be costly. Accurate inventory, centralized visibility, and automated workflows become essential to maintaining continuous service and trust in a high-frequency certificate environment.
Moving toward automated monitoring
To operate reliably under shorter certificate lifespans, organizations must adopt proactive monitoring and automation. Certificate discovery, expiry alerts, automated renewals, and centralized dashboards are core capabilities that reduce risk and operational overhead. Real-time monitoring helps find certificates issued outside normal IT processes, detect misconfigurations, and track impending expirations so teams can remediate before users are affected.
Consolidating certificate telemetry into a single platform makes it possible to prioritize renewals, detect revocations, and enforce policy across all environments. Automation of renewal and deployment pipelines ensures certificates are rotated before they expire, eliminating the human error that spreadsheets and manual reminders cannot fully prevent.
The era of “set it and forget it” certificate management is over. With the 200-day maximum now in place and further reductions planned, organizations should audit renewal procedures today, build automation, and ensure continuous visibility across all issued certificates. Preparing now will minimize operational disruption and keep services secure as certificate lifespans continue to shorten.