
The digital landscape is constantly evolving, and with it, the strategies for ensuring online security and user trust. Recent changes by leading web browsers like Chrome and Firefox regarding the display of Extended Validation (EV) certificate indicators have sparked considerable discussion and, for many, confusion. What was once a prominent, easily identifiable green bar in the URL displaying a company’s verified name now requires an additional click to access. This shift has led many to question the ongoing relevance and inherent value of EV certificates.
However, contrary to initial assumptions, these browser changes do not diminish the importance of EV certificates. Instead, they highlight a critical need for businesses to understand and leverage the unique benefits of Extended Validation. In an era where cyber threats are more sophisticated than ever, and establishing genuine trust online is paramount, EV certificates remain an indispensable tool for protecting digital assets, safeguarding customer data, and maintaining a strong, credible online presence. This article will delve into why Extended Validation certificates are not just relevant, but more critical than ever, despite their altered visibility.
Decoding the Relocation: Where Did Extended Validation Certificates Go?
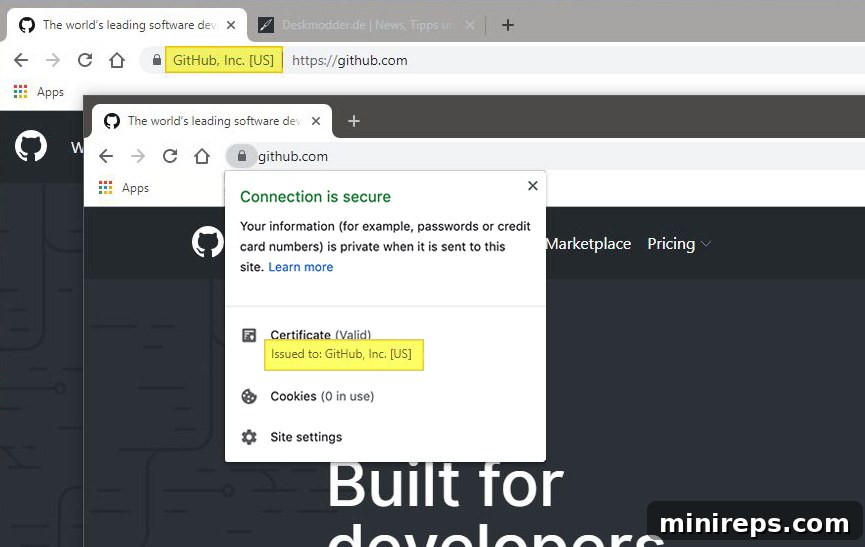
The most visible change concerning Extended Validation certificates began with the Chrome 77 update, quickly followed by similar implementations in Firefox and other browsers. Prior to these updates, websites secured with an EV certificate were easily recognizable by a distinctive green address bar that prominently featured the legally verified name of the organization right in the URL bar, alongside a padlock icon. This clear visual cue served as an immediate, undeniable assurance to users that they were interacting with a legitimate, thoroughly vetted entity, fostering a high level of trust.
With the new browser releases, this prominent display has been moved. To view the EV badge and the detailed organizational information, users must now actively click on the padlock icon located in the URL bar. This action reveals a “Page Info” panel, which then displays the Extended Validation details, including the verified company name. While the information is still accessible, its new, less prominent location has undoubtedly reduced its immediate impact on user perception and awareness. Browser developers contend that this change aims to streamline the user interface and normalize the expectation of a secure HTTPS connection for all websites, without over-emphasizing different levels of SSL validation in the primary display area.
Nevertheless, for businesses operating in sectors where trust, credibility, and definitive identity verification are non-negotiable, this hidden indicator presents a new challenge. It requires a more proactive approach to communicating trust and security, as the instant visual signal of an EV certificate is no longer front and center. Understanding this shift is the first step in adapting business security strategies to ensure that the rigorous validation offered by EV certificates continues to resonate with users and provide essential protection against the evolving landscape of online fraud and impersonation.
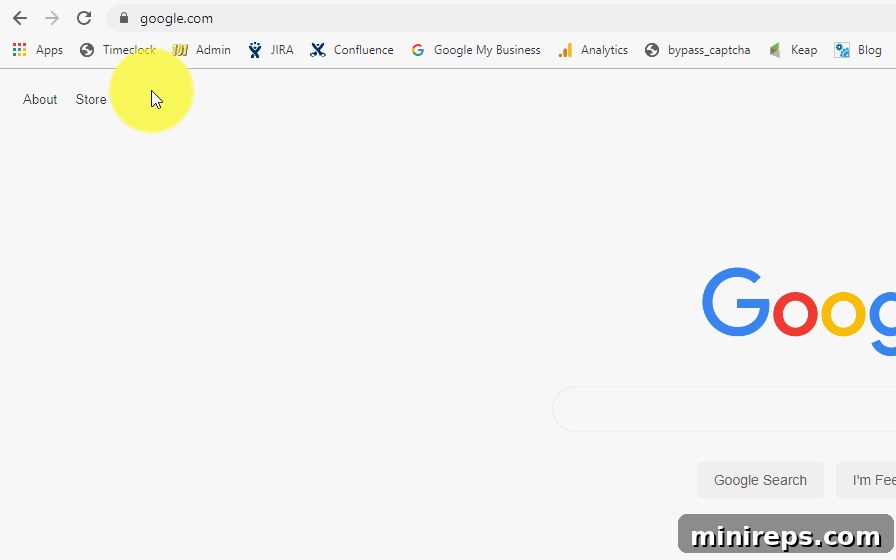
In Chrome 77 and later versions, Extended Validation certificate details are accessed via the “Page Info” panel after clicking the padlock icon in the address bar.
The Browser’s Evolving Strategy: From Reward to Punishment in SSL Security
To fully appreciate the enduring value of Extended Validation certificates, it’s crucial to understand the strategic pivot undertaken by major web browsers regarding SSL adoption. For many years, the primary approach to encouraging website owners to implement SSL encryption was a “reward” system. This involved offering positive incentives such as improved search engine rankings (SEO benefits), increased customer trust, higher conversion rates, and a more professional brand image—all underscored by visible security indicators like the green address bar.
However, despite these clear advantages, universal HTTPS adoption remained elusive. Recognizing this, browsers, led by Google, shifted their strategy towards a “punishment” model. This paradigm fundamentally alters the dynamic, moving away from relying on positive reinforcement for secure practices and instead leveraging negative conditioning to compel widespread SSL implementation across the web. The goal is to make a non-secure website a clear red flag, thereby pushing all site owners towards encryption.

This “punishment” approach manifests through various browser-level deterrents. Websites that do not use SSL encryption are now prominently labeled with “Not Secure” warnings in the address bar, often accompanied by alarming error messages or interstitial warnings that users must bypass to proceed. Browsers also employ other “scare tactics” and increasingly restrictive policies to deter users from visiting unencrypted or inadequately secured websites, particularly those handling sensitive data. By systematically removing positive indicators (like the prominent EV display) and simultaneously amplifying negative warnings for non-secure sites, browsers aim to create a universal expectation of HTTPS. This aggressive push ensures that a basic level of encryption becomes the default for virtually all websites, significantly enhancing baseline web security. However, it also inadvertently homogenizes the perception of security, making it more challenging for the average user to differentiate between a basic Domain Validated (DV) certificate and the rigorous identity verification provided by an Extended Validation certificate. This subtle but profound shift places a greater burden on users and businesses to understand the nuances of digital trust.
Analyzing User Behavior: Do Users Genuinely Care About Extended Validation Certificates?
A central tenet behind the browser’s decision to redesign the user interface and relocate Extended Validation certificate indicators is the controversial assertion that users do not consistently modify their online behavior based on these visible security cues. The argument, frequently articulated by browser development teams, suggests that the presence or absence of specific visual indicators – such as a green padlock, a distinct green address bar, or an organizational name prominently displayed in the URL bar – does not significantly influence users to make more secure choices. For instance, the theory suggests users might still enter sensitive information like passwords or credit card details on a site regardless of whether it shows a basic padlock or a full EV indicator.
This perspective posits that the average user’s behavior isn’t substantially different when encountering various security signals. If visual cues like a prominent green bar or company name don’t consistently translate into more cautious user behavior, then, from a minimalist UI design standpoint, their prominent placement might be considered redundant or even contribute to interface clutter. Consequently, the relocation of the entity name associated with Extended Validation certificates into the less visible “Page Info” section is presented as a logical step to simplify the browser’s interface. This move aligns with a generalized “security by default” philosophy, where all HTTPS connections are treated with a baseline trust, and deeper validation details are available upon request.
While this argument holds some weight regarding the behavior of the least tech-savvy users, it tends to overlook the implicit trust signals that prominent EV indicators provided, especially for businesses operating in high-stakes environments. For many users, even if they couldn’t articulate the difference between SSL types, the green bar and company name conveyed an immediate sense of institutional legitimacy. The absence of such a clear distinction now means that the responsibility for discerning advanced levels of trust falls more heavily on the user, requiring a deliberate action (clicking the padlock) to uncover the validation details. This potential for user complacency or “security fatigue” creates a new challenge for businesses that rely on EV to build and communicate trust effectively.
The Indispensable Value: Why Businesses Must Prioritize Extended Validation Certificates
Despite the changes in how browsers display them, the strategic importance of Extended Validation certificates for businesses has, if anything, intensified. In an era marked by an escalation in cyber threats and an increasingly subtle distinction between legitimate and fraudulent websites, EV certificates offer a profound level of assurance and protection that simpler SSL options cannot replicate. For any business dedicated to safeguarding its customers, preserving its reputation, and securing its financial health, investing in EV is not merely an option but a critical, forward-thinking necessity. Here are five compelling reasons why EV certificates are more vital than ever:
1. A Critical Defense Against the Exploding Threat of Phishing and Brand Impersonation
The proliferation of free and Domain Validated (DV) SSL certificates, while instrumental in achieving widespread HTTPS adoption, has inadvertently created a fertile ground for cybercriminals. Phishers and malicious actors can now effortlessly obtain a basic DV SSL certificate for their fraudulent websites. This immediately removes the alarming “Not Secure” warning in browsers, making their deceptive sites appear ostensibly secure with a padlock icon. This development has made it significantly harder for the average user to distinguish between a legitimate, encrypted business website and a sophisticated, fraudulent one that also displays a padlock. The removal of prominent EV indicators further exacerbates this problem, blurring critical lines of trust and opening the door wider for sophisticated impersonation attacks.
Extended Validation certificates uniquely counter this threat by implementing an exhaustive vetting process. This rigorous verification confirms the legal, operational, and physical existence of an organization, making it virtually impossible for phishers or scammers to obtain an EV certificate for a deceptive or malicious site. By displaying the thoroughly verified organizational name (even if it now requires an extra click to reveal), EV certificates serve as an unparalleled, non-repudiable identifier of a legitimate business’s digital identity. In this challenging new browser landscape, proactively differentiating your digital assets with an EV certificate is not just a best practice; it is an essential, strategic imperative to protect your brand, your customers, and your bottom line from the relentless onslaught of sophisticated phishing and identity theft attempts.
Case Study: PayPal and the Power of EV in Combating Fraud
The global payment giant, PayPal, serves as a quintessential example of a brand under constant siege by phishing attempts. Cybercriminals routinely create elaborate imposter websites, often employing cybersquatted domain names like “pay-pal.com,” “paypal-security-login.net,” or other subtly altered variations. These fraudulent sites are frequently secured with basic DV certificates, meaning they display a padlock icon and appear “secure” at first glance. While these sites can look strikingly convincing and even feature legitimate-looking elements, they fundamentally lack the deep-level identity verification that an EV certificate provides.
This is precisely where the formidable power of EV certificates comes into play. Many advanced phishing filters, enterprise-level security systems, and financial fraud detection mechanisms leverage EV certificate information as a primary means to distinguish authentic corporate sites from malicious counterfeits. These sophisticated systems can query the Extended Validation details for PayPal’s official website, unequivocally confirming that the entity behind the certificate has undergone rigorous vetting and is indeed the correct, legitimate company. This crucial layer of verifiable identity, powered by EV, provides an indispensable defense mechanism against the pervasive threat of online fraud, thereby safeguarding PayPal’s brand integrity, its vast user base, and the broader financial ecosystem.
2. Empowering Users: Shifting Responsibility and the Imperative of Education
As web browsers continue their trend of simplifying user interfaces and relocating critical security indicators, a substantial and undeniable portion of the responsibility for maintaining online safety increasingly falls upon the user. While businesses can invest in the most robust security measures, such as top-tier Extended Validation certificates, the efficacy of these protections is inherently linked to users’ ability to recognize, understand, and utilize the available security signals. By making these critical indicators less prominent and requiring additional steps to access them, browsers are inadvertently creating a more challenging environment for users to make informed security decisions and discern true legitimacy.
This evolving landscape places a heightened and urgent burden on businesses. It’s no longer sufficient merely to adopt superior security measures; companies must now proactively embrace the role of educators for their customer base. Businesses need to actively help users understand the nuances between different types of SSL certificates, the critical importance of actively checking the “Page Info” panel for EV details, and the inherent risks associated with engaging with websites that lack such comprehensive identity verification. This proactive, educational approach ensures that a business’s significant investment in high-level security, like EV certificates, translates into tangible user confidence, enhanced protection, and a collective commitment to online safety, fostering a more informed and secure digital ecosystem.
3. Extended Validation Certificates: Essential for Comprehensive Risk Management and Robust Liability Protection
The notion that all SSL certificates are fundamentally interchangeable because they provide a basic level of encryption is a perilous oversimplification. Extended Validation certificates distinctly differentiate themselves through their meticulously enhanced vetting processes and the robust liability protections they confer—features that are absolutely critical for businesses committed to comprehensive risk management. Unlike rudimentary Domain Validated (DV) SSL certificates, which merely confirm control over a domain name, EV certificates mandate an exhaustive verification of an organization’s legal, operational, and physical existence. This rigorous process significantly minimizes the risk of certificate misissuance, a potential vulnerability for any online entity.
A cornerstone of EV certificates is the substantial warranties they carry. These warranties offer crucial financial protection to certificate holders and, in some scenarios, even to end-users, against financial losses incurred due to a misissued certificate—meaning a certificate erroneously granted to a fraudulent entity impersonating a legitimate business. While these warranties typically do not cover user-side errors or internal security lapses, they provide a vital safety net against failures within the certificate issuance process itself, offering peace of mind to stakeholders. For businesses that routinely handle sensitive customer data, process high-value financial transactions, or manage invaluable intellectual property, this added layer of financial indemnification is not just beneficial, but invaluable for managing enterprise-level risk.
The infamous Equifax data breach, a catastrophic event partly attributed to an expired SSL certificate, starkly illustrates the immense financial, legal, and reputational damage that can result from inadequate certificate lifecycle management. While an SSL warranty does not directly cover internal operational oversights like expired certificates, such incidents underscore the absolute necessity of robust certificate management, a domain where EV certificates often shine. Extended Validation certificates are frequently integrated into sophisticated certificate management platforms, which provide greater visibility, automation, and control over an organization’s entire certificate portfolio, thereby mitigating such significant risks. Reputable Certificate Authorities, such as Sectigo, offer EV warranties ranging from a substantial $10,000 up to an impressive $2 million. This tiered approach allows businesses to select a level of financial protection that is precisely commensurate with their specific operational risks, industry exposure, and compliance requirements. This commitment to higher warranties unequivocally underscores the rigorous standards behind EV and its indispensable role in protecting a company’s critical “asse(t)s” in the broadest, most comprehensive sense.
Explore Advanced Security Options for Your Business
4. Unparalleled Control, Visibility, and Streamlined Functionality for Enterprise Environments
For large organizations, enterprises, and corporations managing an expansive digital footprint, Extended Validation certificates transcend mere strong encryption. They deliver unparalleled control, comprehensive visibility, and significantly streamlined functionality across their entire certificate ecosystem. In complex corporate environments, where hundreds, or even thousands, of certificates may be deployed across a diverse array of domains, subdomains, applications, and internal systems, manual certificate management quickly becomes an insurmountable, error-prone, and resource-intensive challenge.
EV certificates are almost invariably issued through advanced platforms that incorporate robust certificate lifecycle management (CLM) tools. These sophisticated tools empower organizations with centralized control, enabling them to efficiently monitor the status of all their certificates, automate renewals, revoke compromised certificates, and manage the deployment of certificates from a single, intuitive dashboard. This enhanced, holistic visibility is crucial for preventing critical operational errors, such as unexpected certificate expirations (a common cause of costly service outages and severe security vulnerabilities), detecting and preventing the issuance of unauthorized certificates, or ensuring the timely update of cryptographic standards across the entire infrastructure. Industry research suggests that for organizations managing portfolios exceeding 50 domains, the manual maintenance of certificates can consume upwards of 250 hours annually. By streamlining the entire certificate purchase process, automating routine tasks, and providing comprehensive management capabilities, EV solutions dramatically reduce administrative overhead, realize significant time and cost savings, and fundamentally enhance the overall security posture and operational resilience of an enterprise. This granular level of control and automation is absolutely vital for maintaining continuous, secure operations and rigorously adhering to both stringent internal governance policies and complex external compliance requirements.
5. Meeting Critical Compliance Standards: When Extended Validation Certificates Are Mandatory
Beyond the inherent advantages of enhanced trust and superior security, Extended Validation certificates are frequently a non-negotiable prerequisite for adherence to a myriad of industry-specific regulations, national laws, and international compliance frameworks. Organizations operating in highly regulated sectors such as finance, healthcare, e-commerce, and government services are subject to incredibly stringent mandates designed to protect sensitive data, ensure transaction integrity, and safeguard consumer privacy. These regulatory frameworks include, but are not limited to, the General Data Protection Regulation (GDPR), Payment Card Industry Data Security Standard (PCI DSS), Health Insurance Portability and Accountability Act (HIPAA), California Consumer Privacy Act (CCPA), and Federal Information Processing Standards (FIPS).
Critically, certain frameworks and authoritative bodies explicitly mandate the use of Extended Validation certificates to meet their compliance requirements. A prime example is the European Banking Authority (EBA), which frequently requires EV SSL for financial institutions to ensure the absolute highest level of identity verification and transactional security for online banking and payment services. For banks, credit unions, and other financial entities entrusted with managing individuals’ life savings and sensitive financial data, the ability to definitively and verifiably prove their legitimate identity online is paramount. This stringent requirement underscores why specialized and rigorously verified domain extensions, such as the .bank domain, were specifically created and implemented—to provide an additional, unmistakable layer of verifiable trust and enhanced security for online users interacting with critical financial services.
Consequently, for any enterprise-level company, and particularly those operating within regulated industries, EV SSL certificates are not merely considered a best practice or a discretionary security enhancement; they are often a foundational and mandatory requirement for legal operation, robust risk mitigation, sustained customer confidence, and avoiding severe penalties for non-compliance. Investing in EV ensures that a business meets these vital regulatory obligations, thereby securing its operational longevity and trustworthiness in a highly scrutinized digital world.
In summary, while leading web browsers have indeed altered the immediate visual prominence of Extended Validation certificate indicators, the fundamental value and strategic necessity of EV remain stronger and more critical than ever. For businesses aiming to cultivate unwavering customer trust, establish a verifiable digital identity, provide a robust defense against increasingly sophisticated cyber threats, ensure comprehensive regulatory compliance, and ultimately secure their digital future, investing in EV SSL is an indispensable and proactive strategy. It represents a steadfast commitment to the highest standards of digital identity verification and online security, offering invaluable peace of mind for both organizations and their valued customers in an ever-evolving digital landscape.