
From the President & CEO’s Desk
This post is part of an ongoing series of conversations exploring how we can best serve your and your organization’s needs. We hope you find it insightful!
Securing Your Digital Empire: 101domain’s Triple Threat Protection with Red Sift
Every brand’s journey begins with a foundational step: selecting a name, securing a trademark, and acquiring essential domain names. This initial phase marks the birth of your digital identity. But as your venture expands and its digital footprint grows, what strategic steps are crucial for sustained success and security?
Navigating the Ever-Evolving Cyber Threat Landscape
The reality for any growing business in the digital age is an increasingly hostile and dynamic cyber threat landscape. From the moment the internet and intricate networks were conceived, malicious actors have consistently sought to exploit vulnerabilities within these systems. This persistent threat not only complicates business growth but also adds layers of peril that can undermine years of hard work and investment. Protecting your digital assets is no longer an option but a paramount necessity for survival and prosperity.
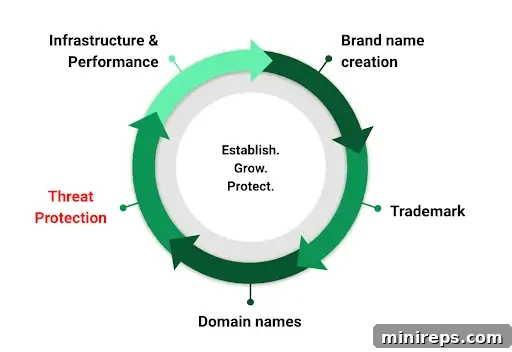
At 101domain, we guide our clients through this complex reality with a clear, actionable philosophy we call Establish. Grow. Protect. This framework is designed to help businesses navigate potential pitfalls and prevent costly cybersecurity incidents.
Establish: Building a Robust Digital Foundation
Businesses excel at establishing their brand in the public sphere. This involves more than just selecting a catchy name; it encompasses strategic trademark registration, ensuring brand uniqueness, and acquiring a foundational portfolio of domain names. A strong establishment phase lays the groundwork for recognition and trust, creating a memorable identity that resonates with your target audience. However, the initial setup is merely the first step in a continuous journey of digital stewardship.
Grow: Expanding Your Digital Presence Responsibly
After successfully establishing a brand, businesses diverge in their approaches to expanding and securing their valuable digital territory. Many focus solely on growth, often overlooking the inherent risks that come with increased visibility. If your digital footprint hasn’t expanded strategically beyond the most common top-level domains like .COM, .NET, and .ORG, you might be unknowingly exposed to significant vulnerabilities. Diversifying your domain portfolio, acquiring country-code TLDs (ccTLDs), and securing brand-specific domains are critical steps in this phase. This expansion should not be an afterthought but a calculated move to enhance reach and reinforce brand presence. To understand more about how we can assist with strategic domain name acquisition, brand protection, and enforcement, you can refer to our previous insights here. The protection of domain names and brands are intrinsically linked, and many businesses unfortunately make the avoidable and costly error of treating domain names as a secondary concern. We are committed to ensuring this isn’t your experience!
Protect: Safeguarding Your Digital Estate
Once your digital presence is established and growing across the domain name landscape, our focus shifts to helping you Protect what you’ve meticulously built. Most modern businesses operate with numerous domain names, each potentially hosting a variety of applications, cloud services, websites, development environments, and networks, all utilizing countless hostnames or sub-domains. As technology rapidly advances, these digital assets can multiply into the hundreds, thousands, or even tens of thousands, quickly becoming incredibly complex and costly to manage and secure.
In the digital realm, much like a physical estate, the more access points (doors, windows, and even hidden passages) your digital infrastructure possesses, the more vulnerable entry points there are for cyber threats. Today’s cybercriminals are remarkably sophisticated, employing diverse tactics to exploit security protocols, or more commonly, lapses in those protocols. Their ultimate goal is to compromise sensitive assets and data. Consequently, adopting a sophisticated and multi-layered approach to cybersecurity is no longer a luxury reserved for large corporations; it is an absolute necessity for businesses of all sizes. The good news is that implementing robust protection doesn’t have to decimate your budget or demand vast internal resources.
The Strategic Advantage: A 101domain and Red Sift Partnership
We are thrilled to announce our strategic partnership with Red Sift, a recognized leader in cybersecurity threat detection and resilience. Together, we offer our clients an integrated platform specifically designed to significantly reduce the cost and complexity of protecting your entire digital estate. This partnership delivers triple threat protection: comprehensively safeguarding your email communications, monitoring your expansive digital attack surface, and ensuring the integrity of your security certificates. This layered defense strategy empowers businesses to proactively identify, assess, and mitigate risks effectively as their technical operations expand, thereby protecting their invaluable brand reputation, retaining customer trust, and securing their financial bottom line.
OnDMARC: Fortifying Email Defenses and Boosting Deliverability
Email remains the single most common vector for cyberattacks. Phishing, sophisticated spoofing, and Business Email Compromise (BEC) attacks relentlessly exploit trust and familiarity. These insidious schemes trick recipients into divulging sensitive information, transferring funds to fraudulent accounts, or clicking malicious links. Red Sift’s OnDMARC solution directly confronts this pervasive challenge by implementing and automating DMARC (Domain-based Message Authentication, Reporting, and Conformance). DMARC builds upon and enhances existing email authentication protocols like SPF (Sender Policy Framework) and DKIM (DomainKeys Identified Mail). It provides a robust, policy-driven framework for verifying the legitimacy of email senders and, crucially, blocking unauthorized emails attempting to impersonate your domain. OnDMARC demystifies the complexities of DMARC, offering real-time, granular insight into your entire email sending operation across all your domain names. This powerful visibility allows you to confidently achieve and maintain DMARC policies at p=reject or p=quarantine, ensuring your legitimate emails are received as intended and malicious ones are blocked.
Real-world applications of OnDMARC:
- Financial institutions and banks leverage OnDMARC to prevent devastating BEC attacks. By enforcing DMARC at the strictest level (p=reject), these organizations ensure that only authorized senders can utilize their domain, effectively blocking fraudulent emails from ever reaching their intended targets. This proactive measure is instrumental in preventing significant financial losses, preserving institutional reputation, and maintaining customer trust.
- E-commerce businesses with extensive email marketing campaigns utilize OnDMARC to dramatically improve email deliverability. By consistently authenticating their emails correctly through DMARC, these companies significantly enhance their sender reputations. This ensures that legitimate marketing and transactional emails bypass spam filters and consistently land in customers’ inboxes, leading to increased customer engagement, higher conversion rates, and ultimately, greater revenue. We have observed email deliverability lifts of up to 40% for our clients!
- Large, complex organizations depend on OnDMARC for unparalleled email visibility and control. Companies with numerous marketing, technical, and communication teams often onboard new email sending services without proper authorization or the necessary SPF and DMARC configurations. OnDMARC promptly alerts you to these rogue senders, allowing you to configure them correctly or reject unauthorized emails. This ensures your email security posture remains current, compliant, and that all your email campaigns successfully reach their intended audiences without compromising security.
Attack Surface Monitoring: Proactive Threat Detection and Mitigation
The modern business attack surface extends far beyond email, encompassing every potential entry point an attacker could exploit. This “attack surface” is analogous to the secure perimeter, doors, and windows of your digital estate. It includes your websites, web applications, cloud infrastructure, APIs, third-party integrations, employee devices, and even forgotten or shadow IT assets. Each of these components presents a potential entry point for attackers, and this surface is constantly evolving with every new deployment, update, or configuration change.
Red Sift’s Attack Surface Monitoring (ASM) solution provides continuous, comprehensive visibility and security assessment across your entire digital footprint. It meticulously scans all public-facing entry points, identifying configurations, IP addresses, and assets you might not even be aware exist. ASM centralizes and organizes all your digital assets within a single, intuitive interface, offering near real-time visibility and enabling rapid response. You receive immediate alerts to newly discovered vulnerabilities, allowing your teams to fix issues and re-scan the asset instantly to verify the remediation. This eliminates the traditional days-long waiting period for full vulnerability scans, dramatically improving operational efficiency for your security staff.
Real-world applications of Attack Surface Monitoring:
- Healthcare providers leverage ASM to ensure stringent compliance with critical regulations like HIPAA. By continuously identifying and mitigating vulnerabilities across their expansive digital infrastructures, providers can effectively safeguard sensitive patient data, prevent costly data breaches, and avoid severe penalties for non-compliance, thereby protecting both their patients and their practice.
- Technology companies utilize ASM to proactively manage risks associated with their rapidly evolving cloud infrastructures. Given the dynamic nature of cloud environments, continuous monitoring of changes, configurations, and deployments is crucial. ASM allows these companies to quickly identify and remediate potential security gaps, ensuring the integrity, availability, and performance of their critical services and applications without interruption.
- During rigorous security compliance audits, companies rely on ASM’s robust reporting and visibility capabilities to expedite evidence generation. Auditors frequently demand a wide array of reports, screenshots, and demonstrations to confirm adherence to security standards. ASM securely provides this comprehensive visibility in a streamlined manner, saving countless hours, alleviating frustrations for all parties involved, and eliminating the need for various traditional and custom-built tools or manual scripts previously used for this purpose.
Certificate Monitoring: Ensuring the Security and Integrity of SSL/TLS Certificates
SSL/TLS certificates are the bedrock of secure communication channels and are absolutely fundamental for protecting data transmitted online. They encrypt traffic, authenticate server identity, and assure users that their connection is secure. Expired, misconfigured, or compromised certificates can lead to catastrophic website outages, severe data breaches, browser warnings that deter visitors, and a rapid erosion of customer trust. Red Sift’s Certificate Monitoring solution offers real-time discovery, continuous monitoring, and comprehensive management of all SSL/TLS certificates associated with your domains and subdomains, whether they are used externally, internally, or even managed by your third-party vendors.
Real-world applications of Certificate Monitoring:
- Online retailers depend on Certificate Monitoring to prevent disruptive website downtime and maintain unwavering customer confidence. By receiving proactive alerts for upcoming certificate expirations, retailers can ensure seamless and timely certificate renewals, thereby avoiding service interruptions, preventing potential revenue loss from inaccessible sites, and preserving a secure shopping experience for their customers.
- Financial institutions employ Certificate Monitoring to robustly protect against sophisticated man-in-the-middle attacks. By continuously monitoring for any anomalies or unauthorized changes in their certificates, institutions can rapidly detect and respond to compromised certificates. This critical vigilance prevents attackers from intercepting sensitive customer data, protecting financial transactions and maintaining the integrity of banking services.
- Companies proactively identify and neutralize unauthorized SSL Certificates that attempt to impersonate their legitimate websites. These fraudulent certificates are typically deployed in highly deceptive phishing attacks, crafted to trick customers into providing sensitive information such as login credentials, financial details, or personal data. Certificate Monitoring acts as an early warning system, allowing businesses to respond swiftly and mitigate these threats before they can cause widespread damage.
The Power of Integration and a Comprehensive Approach with 101domain and Red Sift
The true strength of our partnership lies in the seamless integration of OnDMARC, Attack Surface Monitoring, and Certificate Monitoring with your existing systems. These solutions effortlessly connect with leading SIEM (Security Information and Event Management) and SOAR (Security Orchestration, Automation, and Response) platforms, major cloud providers, and various email sending services. This deep integration enables efficient workflow automation, centralized management of security operations, and a holistic view of your security posture, all without interrupting your current operations or causing any downtime.
At 101domain, our dedicated solutions engineers and customer success team are committed to helping our clients maximize the value of their cybersecurity investments. From the initial onboarding and seamless implementation process to ongoing support and strategic guidance, we provide the expert knowledge and resources necessary to achieve and maintain a robust security posture. We are here to empower you every step of the way, ensuring you have the support you need, precisely when you need it.
By adopting our triple threat protection approach, businesses can establish a proactive, cost-effective, and truly comprehensive cybersecurity strategy. This integrated defense system protects against pervasive email fraud, safeguards systems and extensive attack surfaces from a vast array of constantly evolving threats, and ensures the integrity and availability of all security certificates across your entire organization. This unified approach minimizes overall risk, fosters deep customer trust, enhances operational resilience, and ultimately empowers businesses to work smarter, not harder, enabling them to thrive securely in the dynamic digital age.
Don’t wait for a breach to realize the importance of comprehensive protection. Start reaping the immense benefits of triple threat protection today. Contact us for a free and thorough consultation to assess your needs and tailor the perfect solution.
Sincerely,
Anthony Beltran
President & CEO
101domain.com
